GDPR-Compliant Patient Portal Development for a UK-Based Healthcare Provider to Automate Compliance

Learn how we helped a UK-based healthcare provider modernize its patient portal with centralized consent management, automated DSAR workflows, and a real-time compliance dashboard.

overview_gdpr

Project Overview

A UK-based healthcare provider with 15 clinics and 200,000+ active patients was facing a critical compliance deadline. The General Data Protection Regulation (GDPR) had come into full effect, and their existing patient portal—built on legacy architecture—was not designed to meet its stringent requirements. The portal lacked essential features for managing patient consent, handling data subject access requests (DSARs), and providing the "right to erasure".

Challenges

The existing patient portal was developed before GDPR and was fundamentally incompatible with its requirements. The provider's compliance team identified several critical gaps that put the organization at significant legal and financial risk.

  • line icon

    No Centralized Consent Management

    Patient consent for data processing was scattered across paper forms, email records, and the legacy portal. There was no unified system to capture, store, or audit consent. Staff spent 10+ hours weekly manually processing DSARs, searching for patient data across disconnected systems.

  • line icon

    No Mechanism for "Right to Erasure"

    The portal could not process patient requests for data deletion. Deletion required manual intervention across multiple databases, often taking 30+ days. The provider consistently failed to meet the 30-day statutory deadline for DSARs, risking regulatory action.

  • line icon

    Incomplete Audit Trail

    The portal did not log access to patient data, making it impossible to demonstrate compliance during audits. Patient data was stored across 5+ different systems, making it difficult to provide a complete data record to patients.

  • line icon

    Non-Compliant Data Sharing

    The portal shared patient data with third-party systems without explicit, granular consent. Patients were increasingly concerned about data privacy, leading to complaints and a decline in portal usage.

Solution Delivered

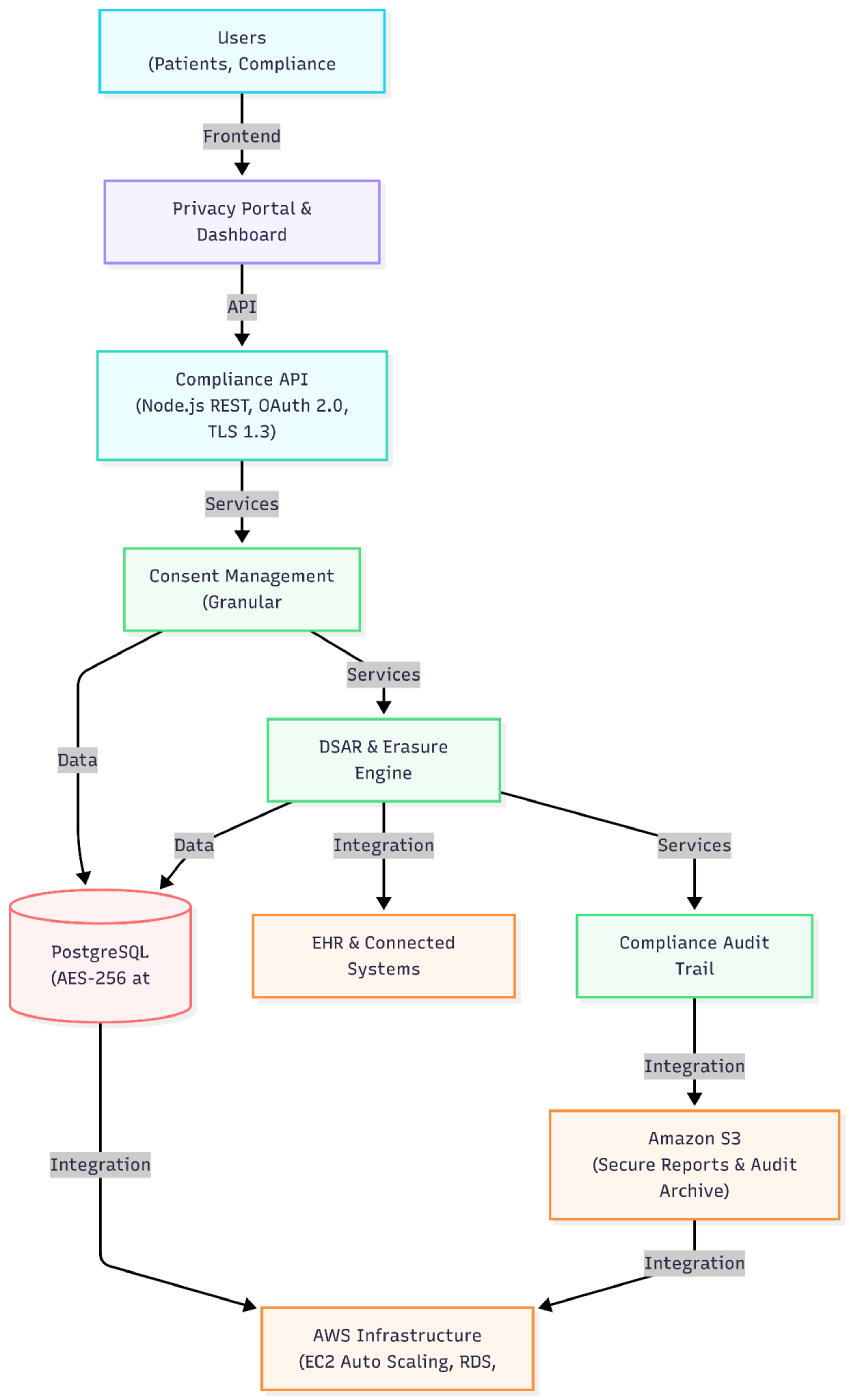
We collaborated with the provider to design and implement a comprehensive, GDPR-compliant patient portal from the ground up. Our solution was built on three core pillars:

Centralized Consent Management Framework

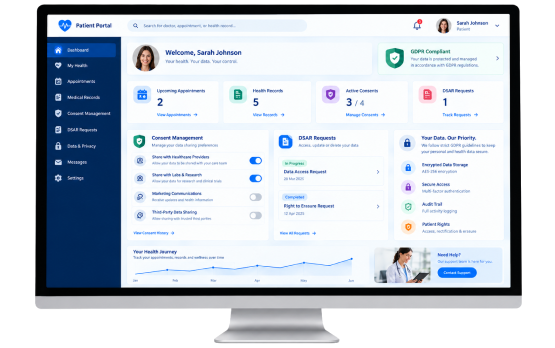
We implemented a granular consent management module that captures, stores, and audits patient consent in real-time. Patients can now manage their consent preferences for specific data processing activities (e.g., sharing with labs, research, marketing) through an intuitive interface. All consent actions are logged with a timestamp and user ID, creating a tamper-proof audit trail.

Automated DSAR & Right to Erasure Engine

We built an automated workflow to handle data subject access requests. Patients can now submit DSARs directly through the portal, which automatically identifies and compiles all relevant data from connected systems into a single, secure report, reducing processing time from 30+ days to under 10 days. The "right to erasure" functionality was also automated, with a verification process to ensure compliance before deletion.

Integrated Compliance Dashboard

We developed a real-time compliance dashboard for the provider's compliance and administrative teams. The dashboard provides visibility into consent status, DSAR processing, and data access logs, enabling proactive management of compliance risks.

Real Numbers. Real Business Impact

DSAR Processing

DSAR processing time was reduced from 30+ days to less than 10 days, exceeding regulatory requirements.

Digital Consent

100% of patient consent preferences are now captured and managed digitally.

Manual Compliance Work

80% reduction in time spent on manual compliance tasks, freeing up staff for patient care.

Portal Usage

Patient portal usage increased by 40%, driven by trust in data privacy.

Compliance Breaches

Zero compliance breaches since implementation, avoiding potential fines of up to €20M.

Technology Stack

Frontend:

React.js for responsive web portal

Backend:

Node.js with RESTful APIs

Database:

PostgreSQL with encryption at rest

Consent Management:

Custom module with tamper-proof audit logging

EHR Integration:

FHIR R4 APIs

Infrastructure:

AWS (EC2, RDS, S3) with auto-scaling

Security:

OAuth 2.0, TLS 1.3, AES-256 encryption

Compliance:

GDPR, UK Data Protection Act 2018

tech stack
×

Conclusion

The GDPR-Compliant Patient Portal project demonstrates how a proactive approach to data privacy can mitigate legal risk while improving patient trust and operational efficiency. By implementing centralized consent management, automated DSAR workflows, and a real-time compliance dashboard, we helped the UK-based healthcare provider achieve full GDPR compliance, reduce manual effort by 80%, and build a foundation for future data privacy requirements.

Beware of Scams

Don't Get Lost in a Crowd by Clicking X

Your App is Just a Click Away!

Fret Not! We have Something to Offer.