






Cybersecurity for an AI SaaS Platform
Business Requirement: An AI SaaS company experienced unauthorized requests to its AI model endpoints, resulting in excessive inference usage and unexpected compute costs. Its existing infrastructure lacked adequate API-level protection, rate limiting, and traffic filtering, leaving model endpoints exposed to automated abuse.
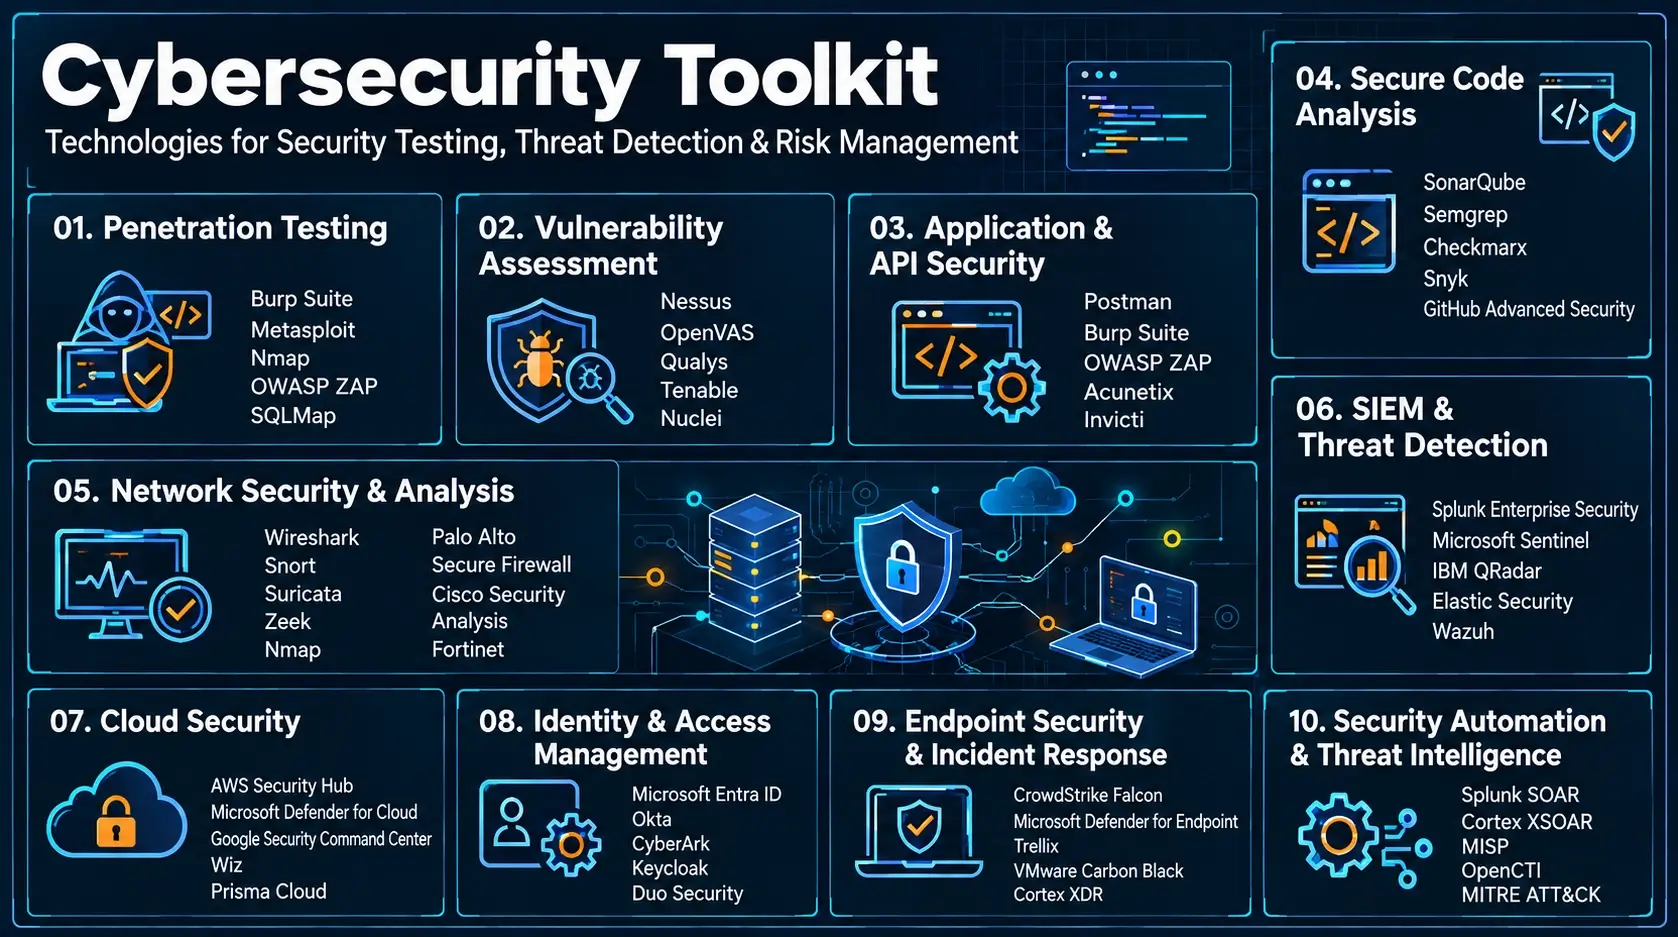
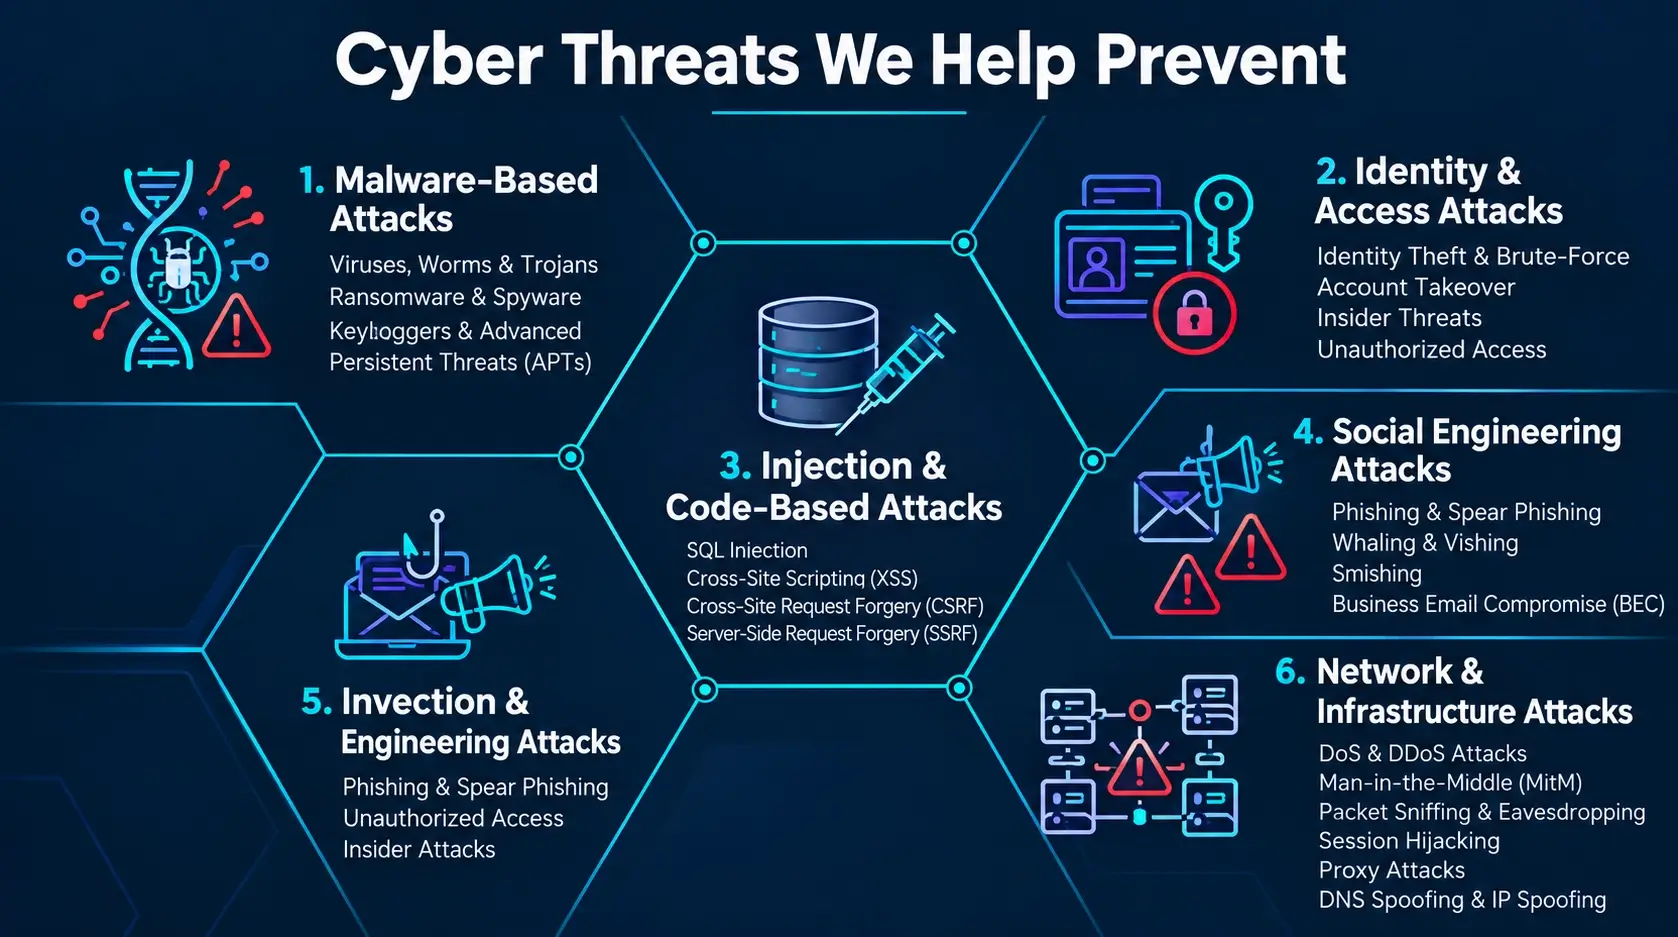
Our Approach: We strengthened the platform's security by implementing a web application firewall (WAF), API gateway controls, request rate limits, and authentication checks. We also recommended monitoring for unusual request patterns, enforcing usage quotas, securing API keys, and alerting the team to suspicious activity.
Outcomes:
- Reduced exposure to automated API abuse.
- Better control over AI model usage and inference costs.
- Improved visibility into unusual traffic and access attempts.
- Stronger protection for model endpoints and API credentials.