+971-8000321216


Key Takeaways
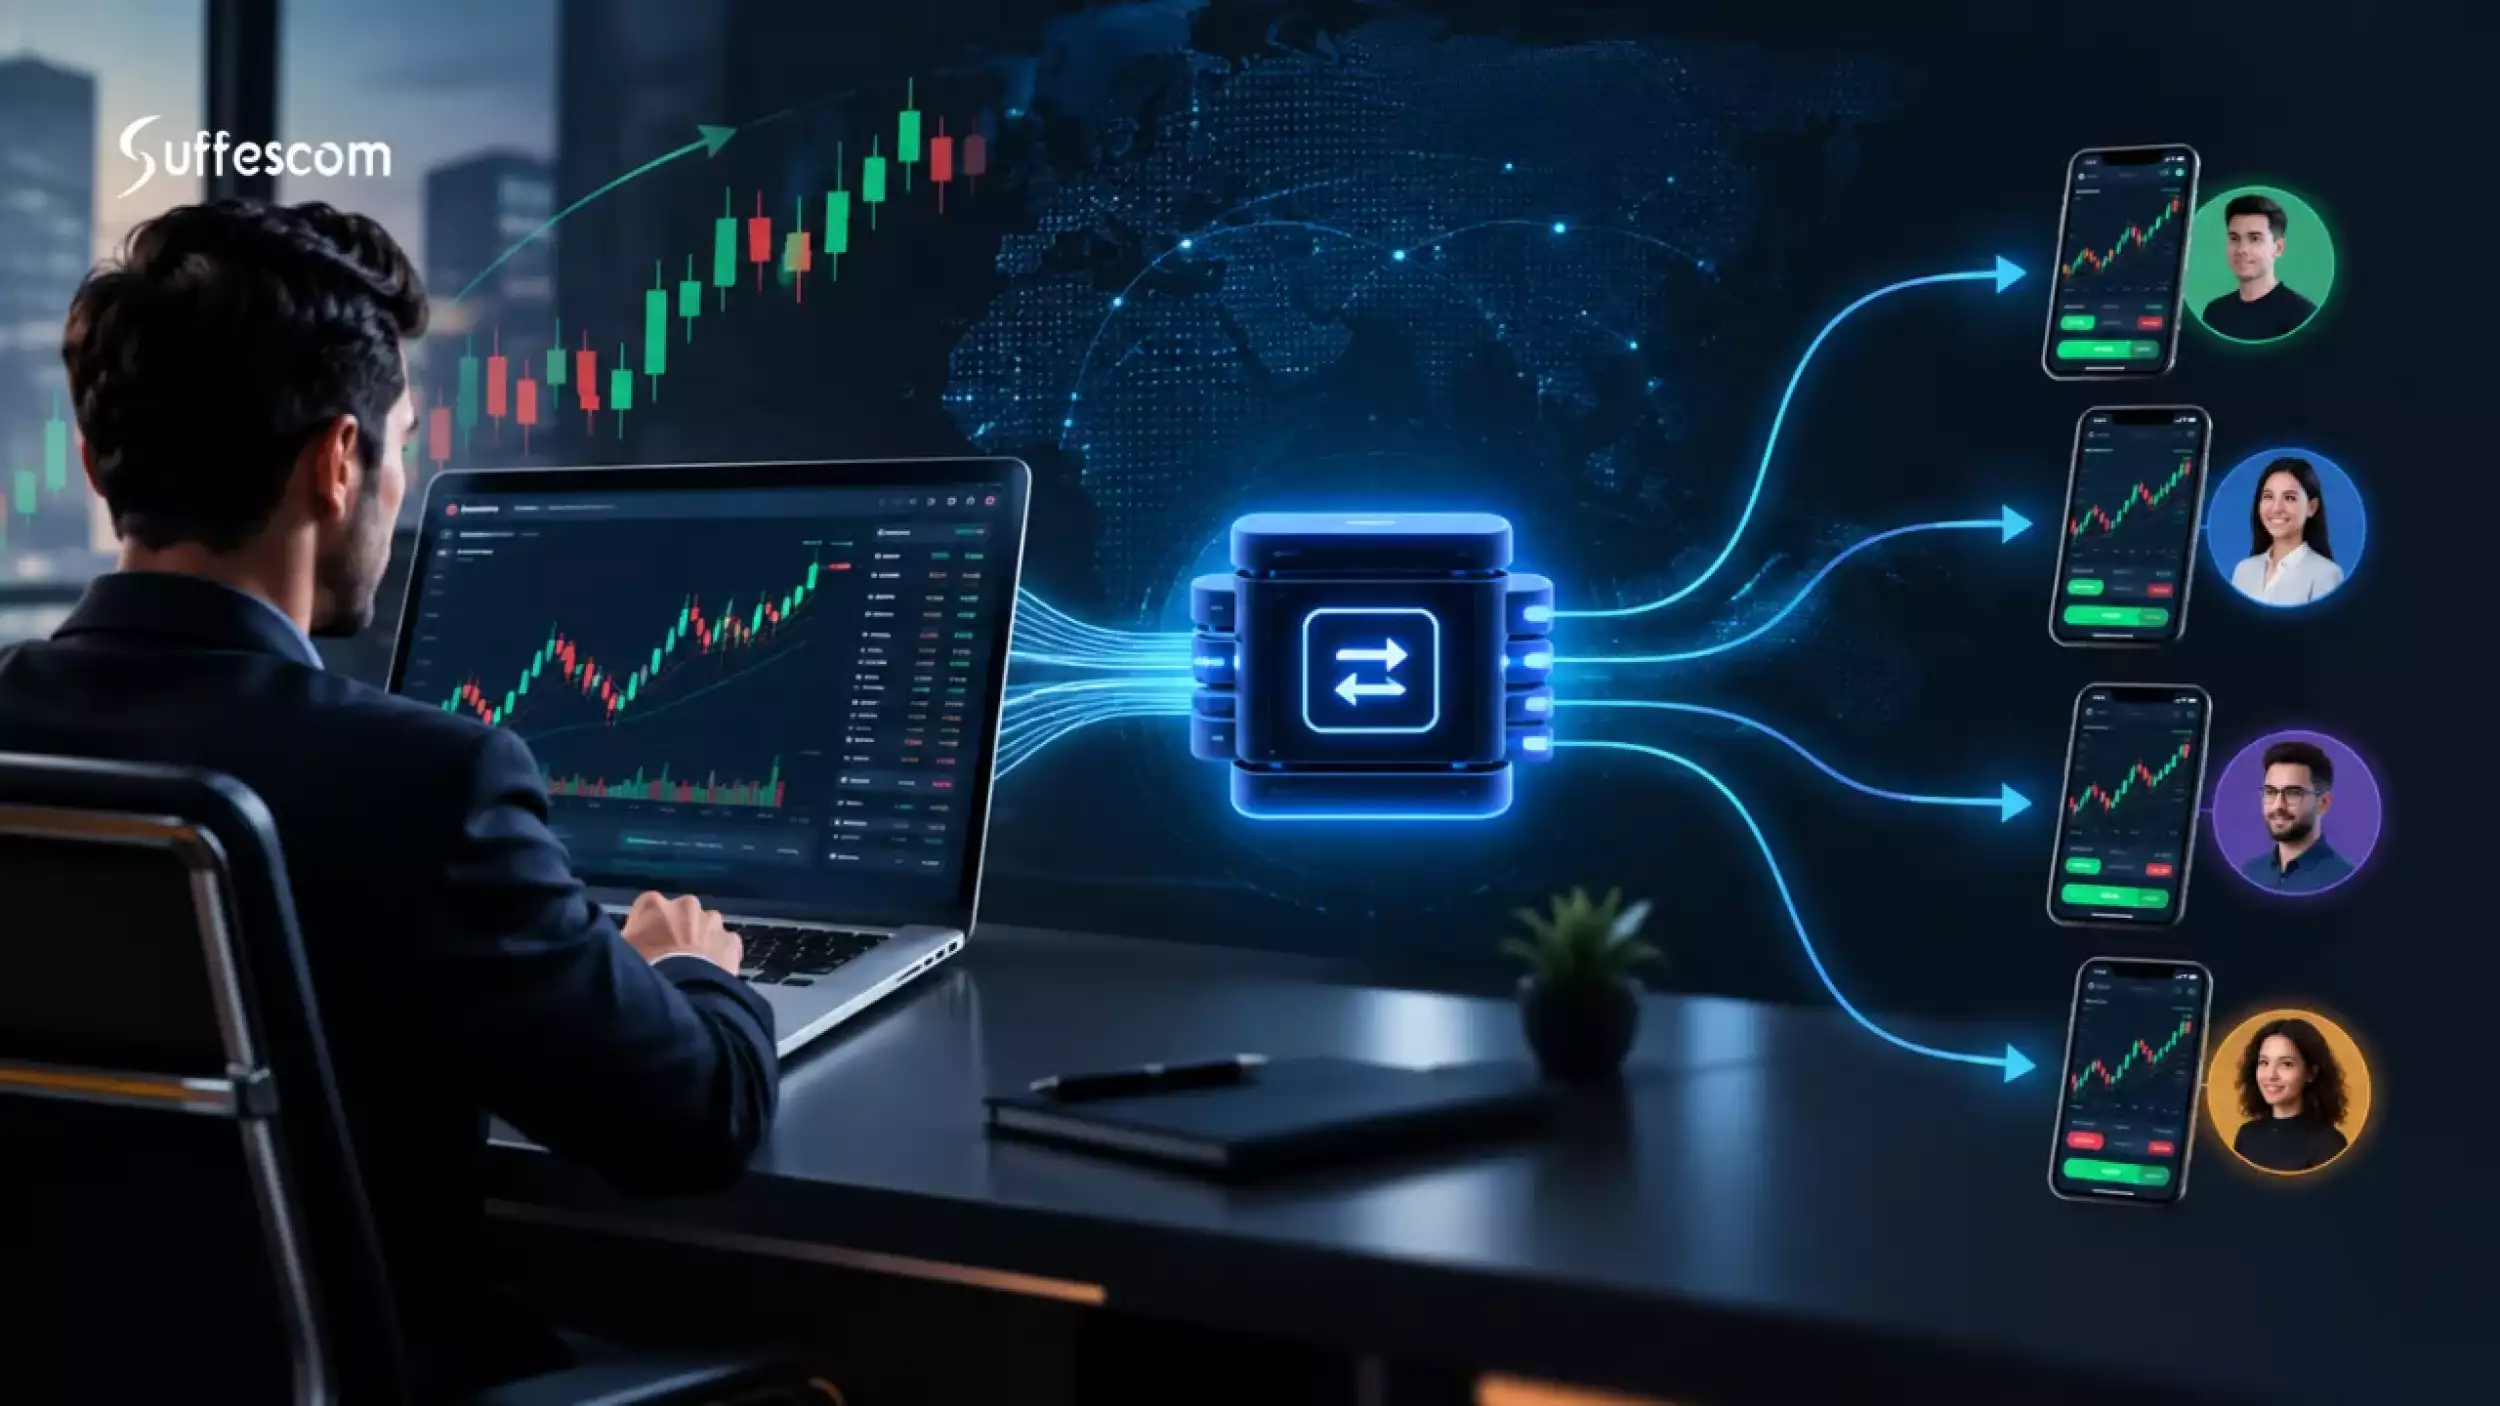
- The engine handles the complete execution lifecycle, capturing leader events, validating them, applying follower-specific rules, translating orders, routing them across brokers, tracking execution, and reconciling positions.
- Event-driven, broker-neutral architecture is essential. WebSockets/FIX, canonical order models, broker adapters, idempotency, queues, and reconciliation help maintain reliable leader-follower trade replication.
- Every follower needs independent risk controls. Multipliers, equity-based sizing, exposure limits, drawdown rules, symbol restrictions, and account-level controls determine whether and how an order is replicated.
- Latency and reliability directly affect execution quality. P50, P95, and P99 latency should be tracked across the execution path, while the engine must handle slippage, partial fills, duplicate events, broker outages, and connection failures.
- The development costs can vary significantly by scope, roughly $40,000–$70,000 for an MVP, $70,000–$150,000 for a multi-broker engine, and $150,000–$300,000+ for enterprise-grade infrastructure. AI-enhanced implementations can exceed $200,000.
- Build progressively, then scale. Start with paper trading and controlled replication, validate risk and reconciliation, and then expand into multiple brokers, larger follower groups, FIX, multi-region execution, and AI-powered monitoring.
Retail trading is no longer a niche digital activity. The latest research found that 45% of investors receive financial advice from the internet, while 24% get investment information from social media, showing how digital channels are increasingly shaping investor behavior.
But turning a trading idea into a reliable follower experience takes much more than forwarding an order. A production-grade master-to-follower execution engine must capture leader events, validate them, calculate account-specific risk, translate orders across brokers, fan them out with low latency, and reconcile every execution. That becomes critical when one leader trade can trigger dozens or hundreds of follower instructions. Slippage, partial fills, broker limits, duplicate events, and connection failures can quickly create execution differences.
Here, we'll explore how to build the underlying execution infrastructure, from architecture and risk controls to latency, recovery, testing, technology choices, and 2026 development costs.
What a Master-to-Follower Execution Engine Actually Does
A master-to-follower execution engine captures trading events from a leader account, evaluates them against predefined rules, converts them into follower-specific instructions, and executes them across connected broker accounts. It does more than duplicate trades. The engine manages risk, execution state, broker differences, failures, and position reconciliation throughout the trade lifecycle.
For master-to-follower execution engine development, the core objective is controlled and traceable trade replication. Every event should have a clear decision path before it reaches a follower.
From One Leader Event to Multiple Follower Executions
The core execution flow is: Leader Broker → Order Event → Event Validation → Strategy/Rule Check → Risk Calculation → Order Translation → Fan-Out → Broker Execution → Confirmation → Position Reconciliation.
The process begins when the leader broker generates an order or execution event. The engine validates the event, checks whether it qualifies for leader-follower trade replication, and applies the follower's trading rules.
Next, the risk multiplier engine determines the appropriate position size. The order is then translated into a broker-compatible format and distributed through the order fan-out system to the selected follower accounts.
After execution, the system records confirmations and compares expected positions with actual broker states. This helps detect execution drift, missing orders, partial fills, or other inconsistencies.
What Makes an Execution Engine Different From a Copy Script
A basic copy script forwards trading instructions. A production execution engine manages the complete execution lifecycle.
| Capability | Basic Copy Script | Execution Engine |
| Connections | Basic | Real-time event handling |
| Order tracking | Minimal | Stateful tracking |
| Risk logic | Usually fixed | Per-account rules |
| Broker support | Limited | Multi-broker |
| Failure recovery | Basic retries | Recovery and reconciliation |
| Idempotency | Often absent | Idempotent order routing |
| Position tracking | Limited | Continuous reconciliation |
| Auditability | Basic logs | Detailed execution records |
| Observability | Server metrics | Execution and latency metrics |
This difference becomes critical as the number of followers and brokers grows. A multi-broker trade copier needs to handle differences in symbols, order types, position models, API responses, and execution rules without changing the core engine.
The Four Execution Decisions the Engine Must Make
For every leader event, the engine needs to answer four questions:
Should this event be copied?
Check the account, instrument, strategy, session, and trading rules.
What should each follower receive?
Translate the leader instruction according to the follower's broker and configuration.
How much should each follower trade?
Apply the risk multiplier engine, equity-based sizing, exposure limits, or other risk rules.
Has the event already been executed?
Use deterministic execution identities and idempotent order routing to prevent duplicate orders during retries or delayed responses.
These decisions turn automated trade replication into a controlled execution workflow rather than simple order forwarding.
Core Terminology
| Term | Meaning |
| Leader/Master | Account whose trading activity is replicated |
| Follower/Child | Account receiving the translated order |
| Copy group | Leader plus its configured followers |
| Fan-out | Distribution of one event to multiple followers |
| Order intent | Normalized instruction derived from a leader event |
| Execution state | Current status of a follower order |
| Risk multiplier | Account-specific position-sizing factor |
| Position reconciliation | Comparing expected and actual follower state |
| Idempotency key | Identifier used to prevent duplicate execution |
| Execution drift | Difference between leader and follower execution |
Define the Execution Model Before Designing the Architecture
The execution model defines when a leader event becomes a replication event and how that event moves through the system. Getting this decision right early prevents major changes to the architecture later.
What Should Trigger a Replication Event?
A replication event can be triggered by different stages of the leader's order lifecycle:
- New order
- Order accepted or filled
- Partial fill
- Order or stop-loss/take-profit modification
- Cancellation
- Position close
- Reversal
The right trigger depends on whether the platform is designed to replicate intent, execution, or position changes.
Order-Based vs. Fill-Based Copying
Order-based copying replicates the leader's order instruction, while fill-based copying replicates what the broker actually executed.
Order-based models can provide faster propagation, but the follower may execute differently or fail to fill. Fill-based models provide stronger execution alignment but can introduce additional execution latency. This decision directly affects the copy trading architecture and reconciliation logic.
Synchronous vs. Asynchronous Execution
The engine can use different execution patterns:
| Model | How It Works |
| Wait-for-confirmation | Confirms one step before continuing |
| Fire-and-track | Sends the order and tracks its result asynchronously |
| Parallel execution | Sends orders to multiple followers simultaneously |
| Queued execution | Places events in a queue for controlled processing |
For high-volume automated trade replication, asynchronous and parallel execution can improve throughput, while queued execution provides greater control during traffic spikes or broker failures.
Full Copy vs. Selective Copy
Selective replication allows each follower or copy group to receive only eligible trades. Rules can filter events by:
- Instrument
- Direction
- Order type
- Trading session
- Strategy identifier
- Account
- Position size
- Risk level
This becomes especially useful for a multi-broker trade copier, where different follower accounts may have different trading permissions and risk limits.
Define the Source of Truth
The architecture should clearly define which system is authoritative at each lifecycle stage. The leader broker can be the source for the original event, the internal execution state can track what the engine intended and processed, and the follower broker can confirm what was actually accepted or executed.
Keeping these states separate makes position reconciliation, failure recovery, and idempotent order routing much more reliable.
Where Master-to-Follower Execution Engines Are Used
A master-to-follower execution engine can power more than a basic trade copier. The architecture remains similar, but follower volume, risk controls, broker connectivity, and compliance requirements change with the business model.
Prop-Firm Trade Replication
Prop firms can use a prop-firm trade copier to distribute approved trading activity across eligible accounts while applying account-specific rules. The engine can calculate different position sizes, enforce drawdown limits, restrict instruments, and isolate accounts that fail execution or risk checks.
Example: A leader opens a 2-lot position. One follower may be configured at 0.5x, another at 1x, while a third account may reject the trade because its exposure limit has already been reached.
Portfolio and Strategy Management
Portfolio managers can use leader-follower infrastructure to distribute strategy instructions across multiple managed accounts without treating every account as identical.
The execution layer of investment platform development can maintain separate risk multipliers, account limits, broker connections, and execution states while keeping the strategy logic centralized.
Trading SaaS Platforms
A commercial trading SaaS product can use the engine as its execution backbone. Multiple leaders can publish strategies while followers select which strategies or trading groups they want to connect to.
The platform can then combine automated trade replication, subscriptions, account management, analytics, risk controls, and broker integrations into one product.
Multi-Account Trading Operations
Businesses managing multiple trading accounts can synchronize selected execution events without forcing every account to use identical quantities or trading rules.
This is particularly useful when accounts have different equity levels, leverage, instruments, broker restrictions, or maximum exposure limits.
White-Label Trade Copier Platforms
Fintech software development companies and trading businesses can build a branded trade copier product around a reusable execution engine. The platform can include custom dashboards, user management, broker integrations, pricing plans, risk controls, and analytics under the company's own brand.
Broker and Fintech Infrastructure
A broker or financial technology development company may use a multi-broker trade copier as an internal execution service or as part of a larger trading ecosystem. In this model, broker adapters, account isolation, observability, reconciliation, and security become particularly important.
The business model determines the architecture. A small internal copier may need one broker and a limited follower group, while a commercial SaaS platform may require multi-tenancy, distributed execution workers, large-scale fan-out, advanced risk controls, and multi-region infrastructure.
Build the Leader Connectivity and Event Ingestion Layer
The leader connectivity layer is the entry point for the entire execution pipeline. It captures trading events from the leader account and provides the data required for validation, replication, and later reconciliation. A reliable design typically combines real-time connections with REST-based recovery and state retrieval.
Broker REST APIs
REST APIs provide on-demand access to broker and account data. They are particularly useful for:
- Account snapshots and current balances
- Historical orders and executions
- Position reconciliation
- Recovering data after a missed real-time event
REST should complement, rather than replace, real-time event connectivity.
WebSocket Connections
WebSockets are typically used for continuous, low-latency event delivery. They can stream:
- New order events
- Execution and fill updates
- Position changes
- Account notifications
This makes WebSockets a key component of an event-driven order execution system where follower actions depend on timely leader events.
FIX Connectivity
FIX becomes relevant when the execution environment requires institutional-grade market connectivity or a broker specifically exposes FIX sessions. It can support structured order and execution messaging where standardized financial-market communication is required.
For enterprise master-to-follower execution engine development, the connectivity strategy should therefore be based on the brokers, asset classes, execution requirements, and infrastructure involved rather than forcing one protocol everywhere.
Connection Lifecycle Management
A persistent trading connection needs active lifecycle management, not just an initial login. The connectivity layer should handle:
- Authentication and credential refresh
- Heartbeats and keepalive messages
- Automatic reconnection
- Session expiration
- Event sequence tracking
- Detection and recovery of missed events
If a connection drops, the system should identify what happened during the gap and recover the missing state before normal replication resumes.
Event Validation
No leader event should enter the execution pipeline without validation. Before processing an event, the engine should:
- Verify the event source and authentication context.
- Validate the message schema and required fields.
- Check the event timestamp.
- Verify sequence continuity.
- Detect duplicate events.
- Confirm the instrument mapping.
This validation layer gives the trade copier engine development process a reliable foundation and helps prevent malformed, duplicated, or incorrectly mapped events from reaching follower accounts.
Build a Canonical Order Model Across Brokers
A multi-broker trade copier should not be allowed to pass a leader broker’s raw order payload to every follower broker. Since every participant may define field names, order types, symbols, quantity, and other contract details differently. A canonical order model creates one broker-neutral representation that the execution engine can translate safely for each destination.
Create a Broker-Neutral Order Object
The canonical order object acts as the common language between the leader and follower brokers. It should capture the information required to reproduce and track the original instruction, including:
- Instrument and side
- Quantity and order type
- Price
- Stop-loss and take-profit
- Time-in-force
- Reduce-only flag
- Position reference
- Leader order ID
- Event ID
- Timestamp
This approach keeps the core copy trading architecture independent of individual broker APIs while allowing each adapter to handle broker-specific requirements.
Normalize Broker-Specific Order Types
The engine should map equivalent order types into a common internal model, including:
- Market orders
- Limit orders
- Stop orders
- Stop-limit orders
- Bracket orders
- OCO orders
For example, a leader's market order should become a standard market-order instruction internally before being translated into the specific format required by each follower broker.
Normalize Symbols and Contract Specifications
Symbol normalization is essential for reliable broker API integration. The system should maintain mappings for:
- Symbol names
- Contract size
- Tick size and value
- Lot size
- Minimum quantity
- Quantity increments
- Exchange-specific naming
This prevents a valid leader instruction from being rejected or incorrectly sized because two brokers represent the same instrument differently.
Preserve the Original Broker Payload
The raw leader event should always be retained alongside the normalized order. It provides the original evidence required for debugging, audits, recovery, and investigating unexpected execution behavior.
Design the Execution Decision Engine
The execution decision engine determines whether, how, and when a leader event becomes a follower order. It connects event validation, account rules, risk controls, and order translation before anything reaches the broker.
Event Validation
The engine first confirms that the incoming event is valid, complete, correctly sequenced, and eligible for processing. Invalid or duplicate events should be stopped before entering the execution path.
Copy Eligibility
Not every leader event needs to reach every follower. Eligibility rules can consider:
- Account mapping
- Instrument
- Direction
- Trading session
- Strategy identifier
- Account status
This allows automated trade replication to remain controlled rather than blindly copying every leader action.
Order Translation
Once an event passes the eligibility checks, the engine converts the canonical instruction into a follower-specific order. Broker capabilities, symbol mappings, account configuration, and existing position state can all influence the final instruction.
Risk Calculation
Follower quantity should be calculated before routing the order. The engine can apply the configured risk multiplier engine, position limits, account-level exposure rules, or other sizing controls to determine the final quantity.
Execution Priority
The engine must also determine how follower orders are dispatched. Depending on the business requirements, accounts may execute:
- In parallel for faster replication
- Sequentially where execution order matters
- Through queues when controlled processing is required
Generate a Unique Execution Intent
Every follower execution should receive a deterministic execution identity. This identifier is required to establish an association between the leader event and specific follower instruction to help achieve idempotent order routing and avoid duplication due to retries, reconnects, delayed responses, and other issues.
The decision layer is the most important element in the reliable master-to-follower execution engine that allows transforming a single leader event into several controlled follower actions.
Build a Reliable Trade Copier, Not Just a Script
Suffescom Solutions can build your execution engine with custom risk controls, broker integrations, and reliable order replication.
Build the Risk Multiplier Engine Around Each Follower Account
A production-grade risk multiplier engine should calculate follower exposure independently instead of blindly copying the leader's position size. Two followers can receive the same leader trade but require completely different quantities because their equity, risk limits, drawdown, broker rules, and trading permissions may differ.
Fixed Quantity Multipliers
Fixed multipliers provide the simplest form of follower-specific sizing. For example:
- Leader = 1.00 lot
- Follower A = 0.50x → 0.50 lot
- Follower B = 1.50x → 1.50 lots
This model works well when followers want predictable scaling. The engine should still enforce each account's maximum order size before approving the final quantity.
Equity-Based Position Scaling
Equity-based scaling adjusts follower exposure according to relative account size. The calculation can consider:
- Leader equity
- Follower equity
- Configured scaling ratio
- Maximum permitted position size
For example, a follower with substantially lower equity should not automatically receive the same absolute position as a much larger account. The resulting quantity is then passed through account-level limits before routing.
Percentage-Risk Replication
Percentage-risk replication focuses on how much capital is at risk rather than copying absolute quantity. The engine can calculate the follower's position using:
- Account equity
- Maximum risk percentage
- Stop-loss distance
- Instrument value
Such an approach is helpful when the follower account has a smaller size than the leader, or the risk management policy requires a lower position size than the one defined in the trading instruction.
Drawdown-Based Scaling
The engine should be able to reduce or stop replication when an account approaches its risk limits. Common triggers include:
- Daily loss threshold reached
- Maximum account drawdown reached
- Maximum exposure reached
For example, an account can move from normal replication to reduced sizing and eventually to a blocked state when predefined thresholds are breached.
Per-Account Trading Rules
Every follower should have its own trading policy. The risk layer can enforce:
- Symbol whitelist or blacklist
- Maximum open positions
- Maximum order size
- Trading-session restrictions
- Long/short direction restrictions
This prevents a valid leader trade from automatically becoming an invalid follower trade.
Risk Decision Before Order Fan-Out
The risk engine should make an explicit decision before an order enters the fan-out stage:
Approved → Modified → Rejected → Requires Review
An Approved order can proceed unchanged. Modified means the engine has adjusted quantity or other parameters to meet the follower's rules. Rejected stops the trade, while Requires Review can route exceptional cases for controlled handling.
This decision-first approach makes the risk multiplier engine a core part of reliable master-to-follower execution engine development, rather than an afterthought added around the order-routing layer.
Model the Complete Order and Position Lifecycle
A production-grade execution engine is not finished when an order is submitted. It must track what happens next, update the follower's state as broker events arrive, and handle failures without losing the relationship between the leader event and follower position.
New Order
When a leader event qualifies for replication, the engine creates a follower-specific order intent with its own execution identity, quantity, and broker instructions.
Order Accepted
The follower broker confirms that it has accepted the order. The engine records the broker's response and moves the order into its active execution state.
Partial Fill
A partial fill means only part of the requested quantity has executed. The engine must track the filled and remaining quantities and determine whether further execution is required.
Full Fill
Once the complete quantity is executed, the follower order moves to a filled state. The resulting position becomes part of the state used for later reconciliation.
Rejected
A reject event may occur if the follower broker declines the order due to insufficient funds, invalid input, market conditions, restrictions, or other reasons.
Cancelled
Cancelled orders should be matched to the corresponding execution event to indicate whether they were cancelled by the engine, broker, or another party.
Expired
An expired order is a valid request that was not executed due to time constraints. The engine should record the expiration and prevent the system from treating the order as successfully replicated.
Modified
Modified orders are updated counterparties of the original trade that should be additionally validated and stored as a separate entry in the log.
Position Opened
A successful fill can create a new follower position. The engine records the resulting position against the relevant leader and execution references.
Position Reduced
Partial closes or reductions must update the follower's remaining quantity without incorrectly treating the position as fully closed.
Position Closed
When the remaining quantity reaches zero, the position moves to a closed state and should be reconciled with the broker's actual position.
Position Reversed
A reversal changes the direction of an existing position. The engine should model the close and new directional exposure correctly rather than treating the reversal as a simple quantity update.
State Machine
The execution state machine provides a controlled path through the order lifecycle:
Received → Validated → Approved → Routed → Accepted → Partially Filled → Filled → Reconciled
Failure paths should be explicit:
Rejected → Retryable / Non-Retryable → Quarantined
This stateful model is essential for leader-follower trade replication because the engine must always know what it expected to happen, what the broker actually reported, and what action should happen next. It also supports reliable reconciliation, recovery, auditability, and idempotent order routing across the entire execution pipeline.
Replicate More Than Entry Orders
A production execution engine must replicate the complete position lifecycle, not just the initial entry. Stop-losses, take-profits, partial closes, modifications, cancellations, and reversals can all change the follower's final exposure.
Stop-Loss Replication
When the leader changes or triggers a stop-loss, the engine should identify the linked follower positions and propagate the required action. Each follower order must still pass through its own broker and risk rules.
Take-Profit Replication
Take-profit changes should remain linked to the original leader and follower execution identities. This allows the engine to update or close the corresponding follower exposure without creating unrelated orders.
Bracket Order Replication
Bracket orders combine an entry with protective exits. The engine should preserve the relationship between the entry, stop-loss, and take-profit when translating the order for different brokers.
Partial Close Replication
A leader may close only part of a position. The engine must calculate the corresponding follower quantity and update each follower's remaining exposure rather than treating the event as a complete closure.
Position Modification
Changes to quantity, price, stop-loss, or take-profit should be treated as lifecycle events and routed to the correct follower orders. Broker-specific capabilities must be considered before applying the modification.
Cancellation Propagation
A cancelled leader order should not remain active on followers. The engine should identify which follower orders are still pending and propagate the cancellation where appropriate.
Reversal Propagation
When a leader reverses direction, the engine must correctly handle the existing position before creating the new exposure. This prevents the follower from ending up with unintended positions.
Leader Position Closure
When the leader closes a position, the engine should locate the corresponding follower positions and generate the appropriate closing actions, subject to follower-specific rules.
Handling Followers With Different Position States
Followers will not always have identical positions. One account may be fully filled, another partially filled, and another rejected or disconnected. The execution engine must therefore evaluate each follower independently and reconcile its actual state before applying the next leader event.
Engineer the Order Fan-Out System
The order fan-out system converts one validated leader event into multiple follower execution requests. At scale, this becomes a distributed processing problem where latency, concurrency, broker limits, and individual failures must be controlled.
Sequential Fan-Out
Sequential processing sends the event to followers one at a time.
Advantages:
- Simpler execution control
- Easier debugging and ordering
Limitation: Aggregate execution latency increases with the number of followers.
Parallel Fan-Out
Parallel processing sends eligible follower requests concurrently.
Advantages:
- Lower distribution latency
- Better suited to large follower groups
Challenges:
- Concurrency management
- Broker rate limits
- Partial failures
- Ordering guarantees
For high-volume automated trade replication, parallel fan-out can improve responsiveness, but it requires stronger controls around retries and execution state.
Queue-Based Fan-Out
A queue separates leader-event ingestion from follower execution:
Leader Event → Queue → Follower Execution Workers
Workers can process follower requests independently, retry eligible failures, and provide backpressure when brokers become overloaded.
Partitioning
Fan-out workloads can be partitioned by:
- Copy group
- Broker
- Follower
- Instrument
Partitioning helps isolate workloads and scale execution workers without turning the entire system into one processing bottleneck.
Broker Rate Limits
The execution layer should respect each broker's API limits through:
- Token-bucket controls
- Request queues
- Backpressure
- Per-broker concurrency limits
This prevents a large fan-out event from overwhelming a broker and causing widespread rejections.
Isolate Follower Failures
One follower's failure should not automatically stop valid executions for other followers. Each follower request should maintain its own execution state, retry policy, and failure outcome.
This isolation is essential for a scalable multi-broker trade copier, where different brokers and accounts can experience different network conditions, limits, or execution results at the same time.
Latency Engineering for Trade Replication
Execution latency is the time taken for a leader event to travel through the replication pipeline and reach the follower broker. For a production-grade master-to-follower execution engine, reducing latency matters, but measuring every stage matters just as much. A system cannot optimize what it cannot observe.
Break Down the End-to-End Execution Path
The complete path is:
Leader Fill → Event Capture → Transport → Validation → Risk Calculation → Order Translation → Fan-Out → Broker Request → Broker Acceptance
Each stage can introduce delay. Breaking the pipeline into measurable steps helps the engineering team identify whether the bottleneck is the network, application logic, queue, or broker.
Establish a Latency Budget
These measurements turn execution latency into an engineering metric rather than a marketing claim.
| Stage | What to Measure |
| Leader event capture | Event timestamp to receipt |
| Event processing | Receipt to risk decision |
| Risk calculation | Rule evaluation duration |
| Order translation | Normalization duration |
| Queueing | Time waiting for execution |
| Broker submission | Internal request latency |
| Broker response | Submission to acknowledgment |
| End-to-end | Leader fill to follower acknowledgment |
Sources of Execution Latency
Common contributors include:
- Polling intervals
- Network distance
- Broker API response time
- Queue congestion
- Serialization and deserialization
- Database writes
- Risk calculations
- Broker rate limits
- Cloud-region placement
A well-designed event-driven order execution pipeline can reduce unnecessary waiting by processing events as they arrive instead of relying on frequent polling.
VPS and Broker Proximity
Infrastructure proximity can reduce network-related latency. Hosting execution workers closer to the relevant broker infrastructure can shorten network round trips, although the actual improvement depends on the broker, network path, market, and deployment environment.
The goal should be measurable latency optimization, not a guaranteed execution speed.
Instrument the Pipeline
Every leader event should carry timestamps through the execution path. The system can then measure when an event was received, validated, risk-approved, translated, queued, submitted, and acknowledged.
This also helps identify unusual delays and supports troubleshooting when follower execution differs from the leader.
Track P50, P95, and P99 Latency
Average latency alone can hide the slowest and most important executions. Track:
- P50: Typical execution experience
- P95: Performance during slower conditions
- P99: Tail latency and exceptional delays
Manage Slippage and Leader-Follower Execution Drift
A master-to-follower execution engine cannot guarantee identical execution prices across every account. The leader and followers may reach the market at different times, use different brokers, or face different liquidity conditions. A production system should therefore manage the difference rather than pretend it does not exist.
Why Followers Can Fill Differently
Follower execution can vary because of:
- Market movement between leader and follower submission
- Network and execution latency
- Available liquidity
- Broker execution policies
- Account-level restrictions
- Position in the broker's order queue
Even when the same instruction is replicated, the follower may receive a different price, fill time, or quantity.
Define Acceptable Slippage
Slippage rules should be configurable for each strategy, instrument, or follower group. Common controls include:
- Absolute price tolerance
- Tick-based tolerance
- Percentage tolerance
- Maximum permitted deviation
For example, an engine can reject a follower order when the market has moved beyond the configured deviation instead of executing at an unexpectedly poor price.
Slippage Policies
Once the permitted threshold is reached, the engine can apply a defined policy:
Execute → Reprice → Reject → Require Confirmation
The appropriate action depends on the trading strategy and risk requirements. These controls should be evaluated before the order enters the final broker execution stage.
Measure Leader-to-Follower Drift
Execution drift should be measurable, not estimated. The system can track:
- Entry price difference
- Fill-time difference
- Quantity difference
- Execution-status difference
These metrics help identify whether drift is caused by network conditions, broker behavior, liquidity, or the replication pipeline itself.
Make Order Routing Idempotent
Idempotent order routing prevents a single leader event from unintentionally creating multiple follower orders. This becomes critical whenever the engine uses retries because a missing broker response does not necessarily mean the broker failed to execute the request.
Why Retries Can Create Duplicate Orders
Consider this sequence:
- The engine submits a follower order.
- The broker accepts and executes it.
- The network response is lost.
- The engine assumes the request failed.
- The engine retries the same instruction.
- The follower receives a duplicate order.
The problem is simple: transport failure and execution failure are not the same thing.
Generate Deterministic Idempotency Keys
Each follower execution should have a unique, deterministic identity. The key can incorporate:
- Copy group
- Leader event ID
- Follower account
- Execution action
This allows the system to recognize that a retry belongs to an execution that has already been processed.
Store Execution Intent Before Submission
The engine should create durable execution state before submitting the broker request. That record should connect the leader event, follower account, intended action, quantity, and execution identity.
Reconcile Before Retrying
Never retry blindly when the broker's final state is unknown. Before resubmitting, the engine should check available broker order and position data to determine whether the original request was accepted, partially filled, fully filled, or rejected.
This combination of durable intent, deterministic identities, and broker reconciliation makes idempotent order routing a core reliability mechanism for trade copier engine development, particularly when many follower accounts are being executed concurrently.
Build Failure Recovery Into the Execution Engine
Failure recovery should be part of the execution design from day one, not an emergency feature added after deployment. A master-to-follower engine must distinguish between temporary connectivity problems, broker-side rejections, and execution states that require manual intervention.
Leader Connection Failure
When the leader connection drops, the engine should:
- Reconnect automatically
- Identify the missed event range
- Replay available historical events
- Reconcile current positions before resuming replication
This prevents the system from silently missing trades during a connection gap.
Follower Connection Failure
A disconnected follower should be isolated without interrupting healthy accounts. Pending instructions can be queued while the engine reconnects, verifies the follower's current broker state, and determines whether the instruction is still valid before resuming execution.
Broker API Failure
Broker failures should be classified before applying a recovery action:
| Failure Type | Typical Response |
| Temporary | Retry with controlled backoff |
| Rate-limited | Delay and re-queue |
| Authentication failure | Refresh credentials or alert |
| Validation failure | Reject and record |
| Market closed | Wait for eligible session |
| Permanent rejection | Stop retrying and record |
This classification prevents unnecessary retries from creating additional load or duplicate orders.
Partial Fan-Out Failure
Consider one leader and 20 followers where 17 executions succeed and 3 fail. The engine should preserve the 17 successful executions while independently recovering or quarantining the three failed accounts.
One follower failure should never roll back valid executions for unrelated followers.
Dead-Letter Queue
Events that cannot be safely processed automatically should move to a dead-letter queue. Store the original event, execution identity, failure reason, retry history, and relevant broker response so the event can be investigated or manually reprocessed.
Circuit Breakers
A circuit breaker can temporarily stop routing to an unhealthy broker after repeated failures. Other brokers and follower groups should continue operating normally.
This isolation is particularly important in a multi-broker trade copier, where one broker's outage should not become a platform-wide outage.
Need Reliable Real-Time Trade Replication?
Build a resilient execution engine with Suffescom Solutions, designed for latency monitoring, failure recovery, and scalable fan-out.
Reconcile Leader and Follower State After Every Critical Event
Reconciliation verifies what the engine intended to execute against what the broker actually executed. It is the control layer that catches inconsistencies caused by network failures, partial fills, rejected orders, and delayed broker responses.
Position Snapshot Comparison
The engine should compare:
- Expected position
- Actual position
- Quantity
- Average price
- Stop-loss
- Take-profit
A mismatch should generate a reconciliation event rather than being silently ignored.
Detect Execution Drift
Execution drift occurs when follower execution differs from the expected leader-derived state. The system should track differences in quantity, price, order status, and position direction to identify abnormal replication.
Detect Orphaned Positions
An orphaned position exists when a follower has exposure that no longer corresponds to a valid leader or execution intent. These positions require immediate evaluation because they can create uncontrolled risk.
Detect Missing Orders
The engine should identify cases where an expected follower order was never accepted, disappeared from the broker state, or failed to produce the expected position change.
Automatic Repair Policies
Depending on the severity and confidence of the reconciliation result, the engine can:
- Retry the instruction
- Close an excess position
- Recreate a missing protective order
- Quarantine the follower account
- Alert an operator
Repairs should not be automated automatically but should be handled as a policy. When additional exposure is created, due to a corrective action, it can be more harmful than the initial inconsistency.
Human Approval for High-Risk Repairs
High-risk reconciliation actions should support human approval before execution. For example, closing a disputed position or creating a large corrective order may require an operator to review the leader state, follower state, and execution history.
This combination of automated recovery, reconciliation, and controlled human intervention makes the execution engine more resilient without sacrificing operational control.
Design the Execution State Store and Audit Ledger
The state store tells the execution engine what is happening now, while the execution ledger preserves what happened and why. Separating these responsibilities gives a real-time trade replication system both low-latency operations and a reliable historical record.
What Must Be Persisted
The execution ledger should retain enough information to reconstruct every important decision and outcome, including:
- Leader events
- Follower execution intents
- Broker order IDs
- Execution responses
- Position snapshots
- Risk decisions
- Rejections and failure reasons
- Retry attempts
- Reconciliation results
This creates a traceable relationship between the original leader event and every follower action.
Hot State vs Durable State
Redis can hold frequently accessed operational state such as active orders, connection status, locks, and short-lived execution data where fast reads and updates matter.
PostgreSQL can store durable execution records, order relationships, reconciliation results, and audit history. This separation prevents the primary database from becoming the bottleneck for every real-time state change while keeping critical records durable.
Event History and Replay
The system must keep a sufficient amount of information about the events so that it can recreate what was done in an execution. Historical records may be used to determine the last known state of the broker when it disconnects and to aid controlled replay or reconciliation in the case of missing events.
Immutable Execution Records
Critical execution history should not simply be overwritten when a state changes. Instead, preserve the original event, decisions, broker responses, and subsequent state transitions so operators can understand what happened, when it happened, and why the engine took a particular action.
Monitor Execution Performance, Latency, and Broker Health
The concept of production observability is not just about CPU, memory, and server uptime. A metrics control point for a reliable execution engine should indicate if trades are being captured, processed, routed, and reconciled properly.
Execution Metrics
Monitor:
- Event throughput
- Orders per second
- Fan-out size
- Execution success rate
- Rejection rate
- Retry rate
- Slippage
- Position drift
These metrics help identify both normal operating patterns and sudden changes in execution quality.
Latency Metrics
Every major stage of the execution pipeline should have its own latency measurement, including:
- Event ingestion latency
- Risk evaluation latency
- Queue latency
- Broker request latency
- End-to-end execution latency
Monitoring these individually allows for the identification of bottlenecks, which is not possible when monitoring only the overall response time.
Broker Health Monitoring
For every connected broker, monitor:
- Connection status
- API response time
- Error rate
- Rate-limit events
- Authentication failures
This allows the engine to detect an unhealthy broker early and activate appropriate recovery or circuit-breaker policies.
Alerting
Operational alerts should focus on conditions that can affect execution or risk. Trigger alerts for:
- Leader disconnection
- Broker unavailability
- Unusual rejection rates
- Abnormal latency
- Position mismatches
- Excessive slippage
- Risk-limit breaches
With this level of observability, copy trading software development moves beyond simply making trades work. It provides the operational visibility required to run a reliable execution platform at scale.
Security Architecture for Broker Credentials and Trading Accounts
Security needs to be incorporated into the execution architecture and NOT added at the end of the broker connectivity. All components should have only the credentials and permissions needed to perform their functions, including access to order instructions and potentially sensitive trading data, which is managed by a master-to-follower platform.
Credential Vault
Raw broker credentials should only be contained within a separate credential vault. API keys and secrets should be grant-scoped or short-lived where possible, rather than hard-coded in the application, stored in a database, logged, or in an application configuration file.
Encryption at Rest and in Transit
Secure sensitive information and trading data in financial software while it's stored and sent. TLS should secure the communication between all users, services, broker APIs, WebSocket connections, and other execution components.
Token Rotation
Controlled rotation and revocation of broker tokens and credentials should be supported. Rotation is a way to mitigate the effect of potentially lost credentials and should be possible without additional downtime in the execution pipeline.
Least-Privilege Access
Each service should receive only the permissions required for its role. A monitoring service, for example, should not automatically have permission to submit or cancel trading orders.
Separate Credentials by Broker and Account
Keep credentials logically isolated by broker, account, and execution environment. A problem with one credential set should not expose unrelated follower accounts or brokers.
Administrative Access Controls
Implement robust authentication, role-based access, and extra security measures for critical administrative tasks, including risk limit adjustments, adding a new broker, and account deactivation.
Audit Every Sensitive Action
Document who took sensitive actions, what changed, when, and who affected the account or broker. These audit records should be guarded against unauthorized changes.
Protect WebSocket and FIX Sessions
Real-time execution sessions require the same security discipline as REST-based broker connections. Protect authentication material, validate session state, enforce secure transport, monitor unexpected disconnects, and prevent unauthorized services from accessing active execution channels.
Local, VPS, Cloud, or Hybrid Execution Architecture?
The right deployment model depends on control, scale, broker proximity, and operational requirements. A small private copier may not need the same infrastructure as a SaaS platform serving thousands of follower accounts.
Local-First Execution
Local execution can suit users who want direct infrastructure control and minimal cloud dependency.
It is particularly useful when:
- Broker credentials should remain within the user's infrastructure
- Direct infrastructure control is important
- Cloud dependency needs to be minimized
The trade-off is that uptime, monitoring, updates, and recovery become the user's responsibility.
VPS-Based Execution
A VPS provides a persistent environment designed for continuously running execution workers. It can support stable broker connections, dedicated resources, automated restarts, and deployment in a region with suitable broker connectivity.
This model is often practical for smaller or dedicated trade copier engine development deployments without the operational complexity of a large cloud platform.
Cloud Execution
Cloud infrastructure becomes useful when the product needs centralized management, large follower groups, automated scaling, or multi-region deployment.
It can support:
- Centralized account management
- Large follower groups
- Multi-region infrastructure
- SaaS-based trade copier products
However, cloud deployment requires careful handling of credentials, network architecture, regional availability, and execution-worker placement.
Hybrid Architecture
A hybrid model can separate centralized control from latency-sensitive execution.
A typical architecture is:
Cloud Control Plane → Dedicated Execution Workers → Local/VPS Broker Connectors
The cloud layer can manage users, configurations, risk policies, monitoring, and reporting, while dedicated workers handle broker connectivity and order execution closer to the required infrastructure.
Architecture Comparison
| Factor | Local/VPS | Cloud | Hybrid |
| Central management | Limited | Strong | Strong |
| Infrastructure control | High | Medium | High |
| Multi-user SaaS | Difficult | Strong | Strong |
| Broker proximity | Deployment dependent | Region dependent | Configurable |
| Operational complexity | Medium | Medium | High |
For a commercial multi-broker trade copier, deployment should be selected around the execution model rather than infrastructure preference alone. Suffescom Solutions can architect the control plane, execution workers, broker connectors, and security boundaries according to the platform's follower volume, broker mix, and scalability requirements.
Multi-Broker Execution Requires an Adapter Architecture
A multi-broker trade copier should have separate logic from the broker to the connectivity. The authentication mechanisms, symbols, order types, position models, quantity units, margin rules, error codes, and the format of real-time events vary between brokers. It's easy to add a new integration, but it's much more difficult to keep up every time a new broker is added that wants to send a new payload directly through the core engine.
Why One Broker API Cannot Be Treated Like Another
A leader order that works with one broker may require a different payload, symbol mapping, quantity format, or position action at another. Even WebSocket events can use different schemas and lifecycle states.
For reliable broker API integration, the engine should normalize these differences at the adapter layer while keeping risk, routing, reconciliation, and execution logic broker-neutral.
Broker Adapter Interface
Each broker adapter should expose a common execution contract, such as:
connect() → subscribe() → submitOrder() → modifyOrder() → cancelOrder() → getPosition() → reconcile()
The core engine calls these standard methods without needing to understand each broker's internal API. The adapter handles authentication, payload conversion, symbol mapping, response normalization, and broker-specific errors.
Add New Brokers Without Rewriting the Core Engine
A new broker should require a new adapter, not a redesign of the execution engine. This separation makes multi-broker trade copier development easier to test and scale while reducing the risk of introducing broker-specific changes into unrelated execution logic.
It also creates a cleaner path for Suffescom Solutions to add brokers as the product expands into new markets or asset classes.
Broker Capability Registry
Not every broker supports the same execution features. A capability registry should record whether each integration supports:
- Market orders
- OCO orders
- Bracket orders
- Partial closes
- Streaming events
- Position modification
The execution engine can then check these capabilities before generating a follower instruction instead of discovering incompatibilities after submission.
Recommended Technology Stack for Trade Copier Engine Development
The technology stack should be selected around execution requirements, follower volume, broker connectivity, and reliability targets, not around a fixed list of fashionable technologies.
Connectivity
Use the connectivity method supported by each broker and required by the execution model:
- REST APIs for snapshots, recovery, and account data
- WebSockets for real-time events
- FIX for institutional connectivity where supported
- Broker SDKs where they provide useful native capabilities
This combination gives the WebSocket/FIX execution pipeline both real-time event handling and reliable state-recovery options.
Backend
Go is a great option for concurrent execution-related services and services that require a lot of network communication. For API and event-driven applications, Node.js can be a good choice, and Rust might be suitable for parts of the application where the control over performance and resource consumption is worth the extra development complexities.
The right choice depends on the execution path rather than language preference.
Messaging
For event transport and order fan-out system design, common options include:
- Redis Streams: Appropriate for lightweight event processing and smaller/mid-sized deployments.
- Kafka: Appropriate for event streaming and replay that needs to be durable and high throughput.
- NATS: Useful where lightweight, low-overhead event transport is preferred
The messaging layer should support the required delivery guarantees, throughput, ordering, and recovery model.
Data
PostgreSQL can provide durable execution records, account configuration, order relationships, and audit history. Redis can handle low-latency operational state, caching, locks, and other short-lived execution data.
Separating the hot operational state from durable records keeps the execution path responsive without sacrificing traceability.
Infrastructure
Use Docker to package execution services consistently across environments. Kubernetes can become valuable for larger deployments that need automated workload management, scaling, and resilient service operation.
For larger copy trading software development projects, cloud load balancing and regional execution workers can help distribute control-plane traffic and place latency-sensitive workers closer to relevant broker infrastructure.
Monitoring
A production execution engine should provide metrics, logs, and traces for all of the key services. Prometheus is built to handle time-series metrics, queries, and alerts, which includes monitoring execution throughput, latency, errors, and broker health.
A practical monitoring layer can include:
- Prometheus for metrics
- Grafana for dashboards
- Centralized logs for investigation
- Distributed tracing for cross-service execution paths
Technology Selection Principle
No single stack is mandatory for every trade copier. Choose technologies based on:
- Number of followers
- Number of brokers
- Required execution latency
- Reliability and recovery requirements
- Expected event throughput
- Deployment model
- Team expertise and maintenance capacity
For example, a private copier serving a small follower group may not need Kafka or Kubernetes. A SaaS platform handling thousands of accounts across multiple brokers may justify a more distributed architecture.
Testing a Master-to-Follower Execution Engine Before Live Trading
Testing should reproduce real execution conditions, not just confirm that APIs respond correctly. A production-ready engine needs to prove that orders, risk rules, failures, and recovery behave correctly under normal and abnormal conditions.
Unit Testing
Test individual execution components such as:
- Risk and quantity calculations
- Symbol and contract mapping
- Order translation
- Quantity conversions
- Idempotency logic
Integration Testing
Test the complete interaction with broker infrastructure, including:
- REST and WebSocket APIs
- Authentication
- Order submission
- Order responses
- Position retrieval and reconciliation
Paper Trading
Run complete leader-follower groups with simulated or paper capital before enabling live execution. This validates the end-to-end replication flow without exposing real funds.
Load Testing
Simulate realistic scale:
- High-frequency leader events
- Large follower groups
- Multiple simultaneous markets
- Broker API throttling
The goal is to identify throughput limits, queue congestion, and concurrency problems before production.
Latency Testing
Measure P50, P95, and P99 latency across the complete path from leader event capture to follower broker acknowledgment. Average latency alone is not enough to understand tail performance.
Chaos Testing
Intentionally introduce failures such as:
- Leader disconnection
- Follower disconnection
- Broker outage
- Network packet loss
- Duplicate or delayed events
- Queue failure
This tests whether the trade copier engine development architecture can continue safely when individual components fail.
Recovery Testing
Only if the failure is repaired and the engine is returned to the correct state will a recovery test be a success. Check reconnection and event replay, reconciliation, retry, and duplicate prevention prior to live trading.
AI Opportunities Inside a Master-to-Follower Execution Engine
AI can supplement a master-to-follower setup, but the decision to execute the actual orders must be left to deterministic controls. Decision support, anomaly detection, risk insights, and operational automation are the strongest application areas.
AI-Based Trade Filtering
AI can analyze factors such as:
- Instrument
- Current trading conditions
- Historical account behavior
- Strategy metadata
It can then provide a filtering signal before an eligible trade enters the normal execution workflow.
Dynamic Risk Adjustment
AI can help identify changing risk conditions and suggest adjustments based on:
- Account drawdown
- Recent performance
- Current exposure
- Market volatility
Any AI-generated adjustment should still pass through explicit risk limits before affecting follower orders.
AI-Based Anomaly Detection
Machine-learning models can flag unusual behavior, including:
- Unexpected order sizes
- Abnormal trading frequency
- Unusual slippage
- Significant position divergence
These signals can trigger additional validation, alerts, or account review.
AI-Assisted Failure Investigation
AI in investment can reduce operational workload by summarizing complex execution incidents. It can correlate broker errors, failed orders, position mismatches, and reconnection events to help operators identify the likely source of a problem faster.
AI Should Not Replace Deterministic Execution Controls
The core execution path should remain:
- Explicit
- Testable
- Reproducible
- Auditable
AI can provide intelligence around the execution engine, but order routing, risk limits, idempotency, and reconciliation should remain governed by deterministic rules. This balance makes copy trading software development more innovative without making critical financial execution dependent on unpredictable model behavior.
Start With the Right Execution Scope
We can help you plan an MVP that is ready to scale into a multi-broker execution platform.
Common Engineering Problems in Trade Copier Development
Reliable trade copier development is largely about handling exceptions without disrupting valid executions. Broker differences, delayed events, partial fills, network failures, and position drift can all affect replication when they are not considered in the architecture from the beginning. At Suffescom Solutions, these conditions should be treated as core engineering requirements rather than edge cases.
Broker API Differences
- Problem: Brokers use different authentication methods, order formats, response structures, and execution rules.
- Technical Cause: There is no universal broker API contract across trading platforms.
- Engineering Response: Use a broker adapter layer with a common interface. Keep authentication, payload conversion, response normalization, and broker-specific error handling inside each adapter instead of the core execution engine.
Symbol and Contract Mapping
- Problem: One instrument may have multiple symbols, different contract sizes, different tick values, and different quantity requirements for various brokers.
- Technical Cause: Brokers and exchanges have their own instrument and contract specifications.
- Engineering Response: Keep a single instrument-mapping layer that checks against symbols, contract requirements, and minimum quantities and increments prior to routing an order.
Slippage
- Problem: A follower may execute at a different price from the leader.
- Technical Cause: Market movement, liquidity, network delay, broker execution policies, and order queue position can change the available execution price.
- Engineering Response: Define configurable slippage thresholds using price, tick, or percentage tolerances. The engine can then execute, reprice, or reject an instruction according to the configured policy.
Partial Fills
- Problem: A follower may execute only part of the requested quantity.
- Technical Cause: Available liquidity or broker execution conditions may prevent the complete order from filling immediately.
- Engineering Response: Monitor and report residual and remaining quantities separately. Reconcile the position of the follower prior to determining if the remainder should be performed, canceled, or monitored.
Duplicate Events
- Problem: The same leader event can enter the execution pipeline more than once.
- Technical Cause: Duplicated broker notifications, message replay, reconnects, and retries may generate duplicate events.
- Engineering Response: Use deterministic event and execution IDs and apply idempotent order routing. When attempting to make an uncertain request, check if the respective follower execution is already defined.
Scenario: When the order is sent to the broker, but the acknowledgment is lost, the engine should recognize the previously executed order.
Lost WebSocket Messages
- Problem: When a connection is interrupted, a real-time event may be missed.
- Technical Cause: Events can be interrupted from delivery due to network failures, session termination, broker disconnects, or sequence gaps.
- Engineering Response: Identify the sequence of events, automatically rejoin them, retrieve lost events via existing historical APIs, and reconcile positions prior to rejoining.
API Rate Limits
- Problems: If there is a big follower group, then there might be more requests than a broker API allows.
- Technical Cause: Brokers have request quotas and concurrency limits to manage API traffic.
- Engineering Response: Use queues, token-bucket controls, backpressure, and per-broker concurrency limits. This allows the order fan-out system to distribute requests without overwhelming a broker.
Position Drift
- Problem: A follower's actual position can differ from the expected replicated state.
- Technical Cause: Rejected orders, partial fills, manual account changes, missed events, or broker-side adjustments can create differences.
- Engineering Response: Run regular position reconciliation and compare quantity, direction, average price, and protective orders. Apply predefined repair, alert, or quarantine policies when material drift is detected.
Network Failures
- Problem: A request may reach the broker while its response never reaches the execution engine.
- Technical Cause: Connection loss, timeouts, routing problems, or infrastructure failures can create an uncertain execution state.
- Engineering Response: Persist the execution intent before submission, use controlled retries, and verify the broker's order or position state before resubmitting an uncertain request.
Inconsistent Order States
- Problem: An order may have been pending internally on the internal engine and may be rejected or canceled by the broker.
- Technical Cause: Broker events may be received out of order, late, or late acknowledged.
- Engineering Response: Maintain a state machine that separates internal intent from broker-reported state. Reconcile conflicting states before taking another execution action.
Scaling the Database
- Problem: High event volumes can generate substantial database reads and writes.
- Technical Cause: Leader events, follower intents, broker responses, retries, and reconciliation records all create persistent data.
- Engineering Response: Separate hot operational state from durable execution records. Use appropriate indexing, connection pooling, batching, and partitioning strategies as transaction volume grows.
Managing Large Numbers of Persistent Connections
- Problem: There are thousands of broker and streaming connections that can take up a lot of memory, network, and CPU resources.
- Technical Cause: Persistent connections require authentication, heartbeats, monitoring, reconnection handling, and lifecycle management.
- Engineering Response: Use asynchronous I/O, efficient connection management, health monitoring, controlled reconnection, and workload partitioning. Regional execution workers can also help distribute connection and broker workloads as the platform scales.
The objective is not to eliminate every failure. It is to ensure that each failure has a predictable response. A good master-follower execution engine will be able to determine when to try again, when to reconcile, when to isolate an account, and when to call on an operator.
How to Develop a Master-to-Follower Execution Engine Step by Step
Building a master-to-follower execution engine requires more than connecting a leader account to multiple follower brokers. The development process should establish the replication model first, then progressively add normalization, risk controls, execution, recovery, and observability.
The following 12-step approach gives Suffescom Solutions a practical framework for developing a scalable and production-ready trade copier engine.
Step 1: Define the Trading and Replication Model
The first step is to determine what can be considered a replication event and when the engine should respond to it. Determine how many of the following events will trigger replication: Order Submitted, Order Accepted, Order Filled, Modification, and Order Closed; and whether it will be synchronous, asynchronous, or queue-based.
The model should also define which instruments, order types, accounts, and trading sessions are eligible for replication.
Step 2: Map Broker Capabilities
Document each broker's authentication method, supported order types, symbol conventions, position model, streaming capabilities, rate limits, and execution features.
This capability map becomes the foundation for the broker adapter architecture and helps the engine identify which instructions can be translated directly and which require broker-specific handling.
Step 3: Define the Canonical Order Model
Create a broker-neutral order object containing the fields required for validation, translation, routing, and tracking.
Common fields are instrument, side, quantity, order type, price, stop loss, take profit, time in force, leader order ID, event ID, and timestamp. This keeps the core execution engine independent of individual broker payload formats.
Step 4: Design Risk and Allocation Rules
Outline the method for determining the size of each follower's order and their exposure. This can include fixed multipliers, equity-based scaling, percentage risk rules, maximum exposure, drawdown control rules, and restrictions on trading for followers.
The risk engine must explicitly decide before routing: approved, modified, rejected, or requires review.
Step 5: Build the Leader Event Layer
Connect via REST, WebSocket, FIX, or broker SDK to capture and validate leader events in real time.
The event layer should provide all support for authentication, heartbeats, reconnect, sequence tracking, duplicate detection, validation of timestamps, and recovery of events that are missed while in the pipeline.
Step 6: Implement the Execution Decision Engine
Decide if an event should be reproduced, what the follower should be given, how much to trade, and whether or not the event has been handled.
This layer brings together eligibility rules, risk computation, order translation, and execution identity into a single controlled decision before fan-out takes place.
Step 7: Build Broker Adapters
Develop independent adapters for each broker that are able to convert the canonical order model into its corresponding API, symbol format, order types, and response format.
With a clean adapter layer, you don't need to re-engineer the core risk, routing, or reconciliation logic if another broker is added.
Step 8: Implement Fan-Out and Queuing
Design the order fan-out system using a parallel, sequential, or queue-based approach based on latency, scale, and reliability needs.
Introduce broker-specific concurrency limits, rate-limit handling, retries, backpressure, and failure isolation to prevent healthy follower accounts from becoming blocked by a slow or unavailable broker.
Step 9: Add State Reconciliation
Compare expected and actual follower orders and positions throughout the execution lifecycle. Detect missing orders, orphaned positions, partial fills, duplicate executions, and execution drift.
Reconciliation should also identify where an automated repair can take place and when an account should be reviewed manually.
Step 10: Add Observability and Audit
Track execution latency, throughput, rejection rates, slippage, broker health, position drift, retries, and fan-out performance.
Maintain a complete execution history linking the leader event to each follower execution intent, broker response, and final position state. This enables the capability for auditability to uncover any unusual results.
Step 11: Test Failure and Recovery Scenarios
Test out broker outages, duplicate events, loss of WebSocket messages, partial fan-out failures, API throttling, network failures, delays, and recovery behavior.
Testing should verify not only that failures are detected but also that the engine returns to the correct state without creating duplicate orders or unintended follower exposure.
Step 12: Launch With Paper Trading and Controlled Rollout
Start with paper trading before introducing live capital. Validate the complete replication lifecycle, including risk decisions, order routing, reconciliation, latency, and recovery.
Then move through a controlled rollout with a limited number of followers, monitored execution metrics, reconciliation checks, and clearly defined rollback procedures. Expand gradually only after the system demonstrates stable execution under expected production conditions.
MVP vs Advanced Master-to-Follower Execution Engine
The right way to build a master-to-follower execution engine is to scale capabilities with execution complexity. An MVP should prove reliable trade replication and state management first, while later versions can introduce deeper risk controls, broker coverage, automation, and enterprise-scale infrastructure.
MVP
The MVP should focus on the core replication lifecycle without introducing unnecessary infrastructure.
Include:
- One leader account
- Limited follower group
- One or two broker integrations
- Market and limit orders
- Basic risk multiplier
- WebSocket-based event capture
- Order and execution tracking
- Position reconciliation
- Basic monitoring dashboard
- Audit log
The MVP's primary objective is reliable leader-to-follower replication. It should demonstrate that an incoming leader event can be validated, risk-checked, translated, routed, tracked, and reconciled across a controlled follower group.
Version 2
Once the core execution path is stable, Version 2 can expand broker coverage and introduce more sophisticated execution controls.
Add:
- Multiple broker integrations
- Advanced risk and allocation rules
- Bracket orders
- Partial-fill handling
- Advanced exception and recovery handling
- Queue-based order fan-out system
- Advanced execution and broker monitoring
At this stage, the platform can support more complex trading strategies and larger follower groups without redesigning the core execution model.
Enterprise Platform
For an enterprise-grade platform, you need infrastructure that is scalable, isolated, resilient, and operationally controlled.
Add:
- Multi-tenant architecture
- Large follower groups
- FIX connectivity
- Multi-region execution
- Advanced risk engine
- AI-assisted monitoring and anomaly detection
- Broker health-based routing
- Disaster recovery
- Advanced execution and business analytics
At this level, trade copier engine development becomes a distributed execution platform rather than a simple replication service. The architecture must support high connection volumes, broker diversity, regional execution requirements, tenant isolation, detailed auditing, and controlled failure recovery.
Choosing the Right Scope
| Capability | MVP | Version 2 | Enterprise |
| Leader accounts | One | Multiple | Multi-tenant |
| Followers | Limited | Larger groups | Large-scale |
| Broker integrations | 1-2 | Multiple | Multi-broker + FIX |
| Risk controls | Basic multiplier | Advanced rules | Advanced risk engine |
| Fan-out | Basic | Queue-based | Distributed |
| Reconciliation | Core | Advanced | Continuous |
| Monitoring | Basic dashboard | Advanced monitoring | AI-assisted observability |
| Infrastructure | Single-region | Scalable | Multi-region + DR |
For most businesses, the MVP should validate execution reliability before adding enterprise complexity. Suffescom Solutions can then evolve the architecture progressively, adding brokers, followers, risk controls, and infrastructure capacity without replacing the core execution engine.
How Much Does Master-to-Follower Execution Engine Development Cost in 2026?
The cost of master development to follow the execution engine can range from around $40,000 to $350,000+ depending on the execution architecture, broker integrations, number of followers, risk controls, infrastructure, and AI needs. The simple copier is available at the bottom level, while the high-volume execution platform with a number of brokers, advanced risk management, FIX connectivity, infrastructure across multiple regions, and AI platforms is on the higher end of the investment.
There is no meaningful single "trade copier development price." The budget should be estimated from the execution workload and technical scope.
What Determines Development Cost?
The biggest cost drivers are:
- Number of broker integrations: Each broker may require a separate adapter, authentication flow, symbol mapping, order model, and testing process.
- WebSocket/FIX requirements: Real-time streaming and institutional FIX connectivity increase engineering and testing complexity.
- Follower count: A system serving 20 accounts has different infrastructure requirements from one serving thousands.
- Risk-engine complexity: Fixed multipliers are simpler than equity scaling, drawdown controls, percentage-risk sizing, and account-level restrictions.
- Order types: Market and limit orders require less work than brackets, OCO, partial closes, modifications, and reversals.
- Fan-out architecture: Queues, worker pools, partitioning, back pressure, and broker-specific concurrency controls may be needed for high-volume replication.
- Real-time requirements: Lower execution latencies and more careful infrastructure and performance engineering are required.
- Cloud/VPS infrastructure: Development and operating costs include regional workers, persistent connections, load balancing, monitoring, and disaster recovery.
- Security: Extends to credential vaults, encryption, access controls, audit trails, and security testing.
- Monitoring and observability: Production systems require execution metrics, tracing, broker health monitoring, and alerting.
- Testing: Financial execution needs integration, load, latency, chaos, recovery, and paper trading tests.
- Front/back-end work: Account management, execution monitoring, risk controls, reconciliation, and audit views within the admin dashboard.
- AI functionality: Anomaly detection, intelligent filtering, dynamic risk insights, and AI-assisted investigation require additional data and ML engineering.
These factors align with the overall trading-platform cost study for 2026, which reveals that integrations, real-time data, security, infrastructure, AI, compliance, and team composition are key cost drivers.
Indicative Development Scope
| Development Scope | Indicative Cost | Typical Complexity |
| Basic Copier MVP | $40,000–$70,000 | One broker, limited followers, basic replication and risk |
| Multi-Broker Execution Engine | $70,000–$150,000 | Multiple adapters, canonical order model, advanced risk and reconciliation |
| Enterprise Execution Platform | $150,000–$300,000+ | High-volume fan-out, fault tolerance, advanced controls and infrastructure |
| AI-Enhanced Platform | $200,000–$350,000+ | Enterprise execution plus AI monitoring, anomaly detection, and intelligent analysis |
What Each Budget Level Typically Includes
$40K–$70K: Basic Copier MVP
Suitable for validating the core business model with:
- One leader
- Limited follower accounts
- One broker integration
- Market and limit orders
- Basic risk multiplier
- WebSocket event capture
- Order tracking
- Position reconciliation
- Basic dashboard
- Audit logging
- Paper-trading environment
$70K–$150K: Multi-Broker Execution Engine
Adds:
- Multiple broker adapters
- Canonical order model
- Advanced risk rules
- Partial-fill handling
- Slippage controls
- Queue-based fan-out
- Idempotent execution
- Advanced reconciliation
- Broker health monitoring
- Failure recovery
$150K–$300K+: Enterprise Execution Platform
Designed for larger commercial deployments with:
- Large follower groups
- Multiple brokers
- FIX connectivity
- Distributed execution workers
- Multi-region infrastructure
- Advanced risk engine
- High-volume event processing
- Disaster recovery
- Advanced observability
- Multi-tenant architecture
$200K–$350K+: AI-Enhanced Platform
The additional investment can cover:
- AI-based anomaly detection
- Intelligent trade filtering
- Dynamic risk insights
- Execution-drift analysis
- AI-assisted incident investigation
- Advanced analytics
- ML infrastructure and model monitoring
AI can materially increase the budget when it involves custom models, real-time inference, additional data pipelines, or agentic execution capabilities. Broader 2026 trading-platform research similarly identifies advanced AI and high-performance execution as significant cost multipliers.
Infrastructure Costs to Account For
Investment platform development cost is only one part of the total investment. A production execution engine also creates recurring infrastructure and third-party expenses.
Budget for:
- VPS or cloud infrastructure
- Regional execution workers
- Broker/API fees where applicable
- Market-data licensing
- Monitoring and observability
- Centralized logging
- Security infrastructure
- Backup and disaster recovery
- Third-party authentication or compliance services
- Ongoing maintenance and performance optimization
The costs of these vary depending on the traffic volume, the region where deployment is taking place, the market, and the broker. Recent cost studies of trading platforms also show that costs for market data licensing, cloud scaling, APIs, security audits, and maintenance are recurring costs that need to be factored into the initial development.
Development Timeline
The development timeline generally increases with the number of brokers, execution complexity, and testing requirements. A practical planning range is:
| Development Phase | Typical Duration |
| Discovery & architecture | 1–2 weeks |
| Broker integration | 2–5 weeks |
| Core execution engine | 4–8 weeks |
| Risk & allocation engine | 2–4 weeks |
| Dashboard & administration | 2–4 weeks |
| Integration & system testing | 2–4 weeks |
| Paper trading & recovery testing | 2–4 weeks |
| Production rollout | 1–2 weeks |
The overall time frame is 3-5 months for a focused MVP, 5-8 months for a multi-broker platform, and 8-12+ months for a complex enterprise deployment.
Have a Trade Copier Idea? Let's Plan It.
Suffescom Solutions can help you define the right architecture, features, integrations, and development scope for your budget.
Why Choose Suffescom for Trade Copier Development
A reliable trade copier is not just an API integration project. It requires careful engineering across real-time event processing, broker connectivity, risk controls, state management, failure recovery, and security. Suffescom Solutions approaches trade copier development as an execution infrastructure project, with the architecture designed around reliability, scalability, and controlled replication.
Broker Integration Experience
Suffescom can design a broker adapter layer that separates broker-specific authentication, symbols, order types, responses, and API limitations from the core execution engine. This makes it easier to add brokers without rebuilding the entire platform.
Real-Time Systems Engineering
Leader events need to move through validation, risk checks, translation, fan-out, and broker execution without unnecessary delays. Our architecture can use WebSockets, asynchronous processing, queues, and regional execution workers according to the required workload.
Financial and Trading Domain Knowledge
The execution model needs to account for market orders, limit orders, partial fills, position modifications, reversals, stop-losses, take-profits, slippage, and execution drift. Suffescom can translate these trading requirements into clear technical workflows and account-level rules.
Distributed Systems Expertise
Large follower groups introduce concurrency, queue management, broker rate limits, persistent connections, and partial failures. We design these components so one slow or failed follower does not unnecessarily interrupt successful executions elsewhere.
Risk Engine Development
Every follower can have different capital, exposure limits, multipliers, trading permissions, and drawdown thresholds. Suffescom can build a dedicated risk layer that evaluates each follower independently before an order enters the execution pipeline.
WebSocket and FIX Experience
Real-time WebSocket connectivity can support streaming order and position events, while FIX can be considered for environments requiring standardized institutional connectivity. The implementation depends on broker capabilities and the required execution model.
Security Engineering
Trading account access and broker credentials need to be well protected. Encrypted credential storage, token rotation, least-privilege access, isolated broker credentials, secure sessions, and detailed audit trails are some of the features of the architecture.
Performance Testing
This could be different if they had 10 followers rather than 1,000 followers. Before going into production, Suffescom can simulate event throughput, fan-out concurrency, P50/P95/P99 latency, API throttling, connection failures, duplicate events, and recovery scenarios.
Questions to Ask a Development Partner
When hiring a development team, don't just inquire about how they will create the dashboard, but about how they will deal with the challenging implementations.
- How will you prevent duplicate orders?
- How will missed events be recovered?
- How will follower failures be isolated?
- How will broker-specific order types be normalized?
- How will execution latency be measured?
- How will position drift be detected?
- How will risk rules be enforced independently per account?
- How will the system behave during broker downtime?
- How will execution history be reconstructed?
If the development partner cannot clearly explain these workflows, the project may be treating trade copying as a simple API task rather than an execution-engineering problem.
Also Read: Stock Trading App Development Companies in USA
Future of Master-to-Follower Execution Engines
The next generation of leader-follower trade replication is likely to focus less on simply copying orders and more on maintaining accurate, observable, and risk-aware execution states.
Continuous Position Reconciliation
Future engines are likely to perform more frequent reconciliation between expected and actual broker positions, allowing execution drift to be identified earlier.
Intelligent Execution Monitoring
Monitoring might even go beyond the levels of uptime to uncover unusual latency, rejection patterns, slippage, connection instability, and follower-level execution anomalies.
AI-Based Anomaly Detection
AI can be used more and more to detect abnormal order size, unusual frequency of trading, unusual position changes, or patterns other than historical trading behavior.
Dynamic Account-Level Risk Controls
Risk controls may become more adaptive, using account exposure, drawdown, volatility, and recent execution conditions to adjust replication rules within predefined boundaries.
Multi-Broker Execution Abstraction
A stronger abstraction layer can allow businesses to manage multiple brokers through a consistent internal execution model while adapters handle broker-specific differences.
Broker-Aware Routing
Future systems may increasingly consider broker health, connectivity, response latency, rate limits, and supported capabilities when determining how execution workloads should be distributed.
Predictive Infrastructure Scaling
As follower groups grow, infrastructure could increasingly scale based on event volume, market activity, connection demand, and expected execution workload rather than reacting only after capacity is reached.
More Autonomous Exception Handling
Engines can make more recovery automation decisions, such as retrying transient failures, quarantining accounts with issues, and starting reconciliation workflows. High-risk activities should continue to have explicit controls in place.
Explainable AI for Execution Operations
Teams might benefit from AI-powered operational tools to gain insights into execution failures, latency points, or the reasons behind the discrepancies in follower state. The order routing logic is to be deterministically, auditably, and independently verifiable.
These are coming trends and not definite skills. The basic idea will be the same: leverage automation and AI to increase visibility, risk management, and operational efficiency while maintaining predictable and auditable critical execution controls.
Turn Your Trading Concept Into a Production-Ready Platform
From broker connectivity to risk management and execution tracking, Suffescom Solutions can build the complete system around your requirements.
Build Your Execution Engine With Suffescom
When you're validating a trade copier MVP, you're expanding to multiple brokers, or designing an enterprise-grade master-to-follower execution engine, the architecture should be rooted in the execution problems that crop up at scale.
From replication logic to a production-ready execution platform, Suffescom Solutions assists with broker connectivity, canonical order modeling, risk calculation, fan-out, reconciliation, observability, security, and controlled rollout.
Do you have an idea for a master-to-follower execution engine? Talk to our team to discuss the architecture, technology stack, development scope, and estimated investment for your project.
FAQs
1. What is a master-to-follower execution engine?
A master-to-follower execution engine listens to trading information from a leader account, modifies the trades with follower-specific rules and risk controls, and sends the trades to all connected follower accounts.
2. What does a trade copier engine do?
It receives a leader event, validates it, determines the follower-specific quantity, interprets the order, and passes it to the right broker adapter.
3. What is the difference between a trade copier and an execution engine?
A simple trade copier deals with copying trades. There's also an execution engine to handle risk, routing, state tracking, idempotency, reconciliation, failure, and multi-broker execution.
4. Is event-driven execution faster than polling?
Generally, yes. The difference between event-driven execution and polling is that the former can execute as soon as an event is published in the broker, whereas the latter may take a time equal to the polling interval plus the API response time.
5. What is the maximum possible latency of a master-to-follower execution engine?
There are various factors that affect latency, such as the broker, network, infrastructure, processing load, and method of execution. It should be measured by the P50 latency, P95 latency, and P99 latency, NOT by speed promise.
6. Are multiple brokers possible on one execution engine?
Yes. A multi-broker trade copier can use broker-specific adapters, which convert a common order model to the API and order format of each broker.
7. How does a risk multiplier work for follower accounts?
A risk multiplier is a value used to adjust the follower's order size based on the leader's order size. For instance, if the 1-lot leader trade is followed by a 1-lot trade, then a 0.5x multiplier “converts” that follower into a 0.5-lot follower.
8. Can every follower use a different position size?
Yes. Each follower can have independent multipliers, equity-based sizing, exposure limits, and risk rules.
9. How does the engine prevent duplicate orders?
It uses deterministic event and execution IDs, idempotent order routing, durable execution state, and broker-state checks before retrying uncertain requests.
10. What will happen if a follower order goes wrong?
The engine stores the failure, categorizes the failure, and can try again, queue up, reconcile, quarantine, or notify an operator based on the failure policy.
11. How are partial fills handled?
The engine tracks filled and remaining quantities separately and reconciles the follower's actual position before taking further action.
12. Can stop-loss and take-profit orders be copied?
Yes. A production trade copier engine can replicate stop-loss, take-profit, bracket, modification, and closure events when supported by the target broker.
13. How does the engine recover after a broker disconnect?
It reconnects, identifies missed events through sequence tracking, retrieves recoverable events where possible, and reconciles the account before resuming execution.
14. What is position reconciliation in a trade copier?
Position reconciliation compares the expected follower state with the actual broker state to detect missing orders, excess positions, quantity differences, or execution drift.
15. How many follower accounts can a trade copier support?
There is no universal limit. Capacity depends on broker APIs, event volume, connection architecture, fan-out design, infrastructure, and required latency.
16. Is FIX required for a trade copier?
No. REST APIs and WebSockets can support many implementations. FIX becomes more relevant when institutional connectivity, standardized messaging, or broker-specific requirements justify it.
17. Can the engine work with prop-firm accounts?
Yes, provided the prop firm and broker permit the required connectivity and trading activity. Account-specific restrictions and risk rules should be enforced before order routing.
18. Can AI be used in a master-to-follower execution engine?
Yes. AI can support anomaly detection, trade filtering, risk insights, execution monitoring, and failure investigation. Core order routing should remain deterministic and auditable.
19. How much does trade copier engine development cost?
The price of a custom trade copier engine can vary from around $40,000 to $350,000+ depending on the integrations with the brokers, number of followers, risk level, infrastructure, and AI needs.
20. How long does it take to develop a custom trade copier?
Depending on scope, integrations, testing, and infrastructure complexity, the focused MVP might take 3-5 months, and the multi-broker and enterprise platform could take 5-12+ months.